Weekly Cyber Intel Brief | 2026-10-12
Weekly Cyber Intel Brief | October 12, 2026
PressContact Blog · 3 minute read
Weekly Cyber Intel Brief | 2026-10-12
**Headline:** Cybersecurity Moves Into the Physical World, Software Supply Chain and Retail Operations
**Meta title:** Weekly Cyber Intel: OT Attacks, GitLab RCE and Retail Incidents | October 12, 2026
**Meta description:** PressContact examines three October 12 cyber threats: French refrigeration attacks, a critical GitLab vulnerability, and a retail network disruption.
Cybersecurity incidents are no longer confined to stolen records or inaccessible webpages. Today's developments show how compromised connected equipment, exposed development infrastructure and enterprise networks can turn security decisions into immediate operational challenges.
1. Cyberattacks Disrupt Refrigeration at French Supermarkets
CERT-FR first issued an alert on October 12 about compromises affecting remote refrigeration controllers. Its updated October 13 bulletin lists Danfoss AK-SM and AK-SC controllers, along with Copeland and Dixell XWEB systems. This later update is identified here explicitly rather than presented as information available on October 12. Exposed remote-management interfaces create operational risks for refrigeration operators.
**Why it matters:** A security failure affecting refrigeration can create food-safety, inventory and business-continuity concerns. Operators need to know how vendor remote access works, who can change equipment settings, and whether an isolated or manual operating mode exists.
**Communications implication:** Incident updates should explain operational effects and customer protections without speculating about the attacker's identity or access method.
[Source: CERT-FR](https://cert.cyber.gouv.fr/alerte/CERTFR-2026-ALE-012/)
2. GitLab Warns of Maximum-Severity Remote Code Execution Vulnerability
GitLab's October 12 security release addressed CVE-2026-97229, a CVSS 10.0 vulnerability in the CI/CD Regular Expression Compiler. Under certain conditions, an unauthenticated user could execute arbitrary code through a specially crafted regular expression in a CI/CD configuration. The advisory identifies fixed versions 19.4.2, 19.3.5 and 19.2.8. This is the October 12 advisory, distinct from the separate October 21 vulnerability. Consult the current GitLab advisory for deployment-specific remediation.
**Why it matters:** Compromise of the continuous-integration system may expose code, credentials, build artifacts and software delivery processes.
**Communications implication:** Response teams should distinguish confirmed exposure of a vulnerable installation from any evidence of exploitation. Avoid calling the incident a breach without forensic confirmation.
[Source: GitLab](https://docs.gitlab.com/releases/patches/patch-release-gitlab-19-4-2-released/)
3. Ahold Delhaize Takes Systems Offline Following Cybersecurity Incident
Ahold Delhaize said on October 12 that it was experiencing a security issue within its network and had taken some systems offline to help protect them while teams assessed and mitigated the issue. The company said its stores remained open and serving customers. Its initial statement did not establish the attack method or data exposure.
**Why it matters:** Deliberate shutdowns can be a necessary containment step, but they also create immediate availability and supply-chain questions.
**Communications implication:** Customers and suppliers need concrete service-impact updates, not just generic reassurances that teams are investigating.
[Source: Ahold Delhaize](https://newsroom.aholddelhaize.com/ahold-delhaize-takes-precautionary-measures-following-cybersecurity-incident/)
The PressContact Perspective
All three developments reinforce the same operational truth: cybersecurity preparedness must be shared across security, infrastructure, legal, facilities, and communications teams. An incident is not fully explained until an organization can answer what changed, what customers or operations experienced, and what evidence supports its recovery claims.
**LinkedIn draft:** Three October 12 security developments put operational resilience under the microscope: attacks on supermarket refrigeration controllers, a high-severity GitLab code-execution warning and a retailer taking systems offline to contain an incident. The communications lesson is straightforward: incident updates need to address the real-world impact, not just the malware or vulnerability label. Read the Weekly Cyber Intel Brief at www.presscontact.com/blog. #Cybersecurity #IncidentResponse #OperationalTechnology
**X draft:** Today's Cyber Intel: connected refrigeration attacks, GitLab RCE warnings and retail network disruption. Cyber risk is operational risk. www.presscontact.com/blog #Cybersecurity
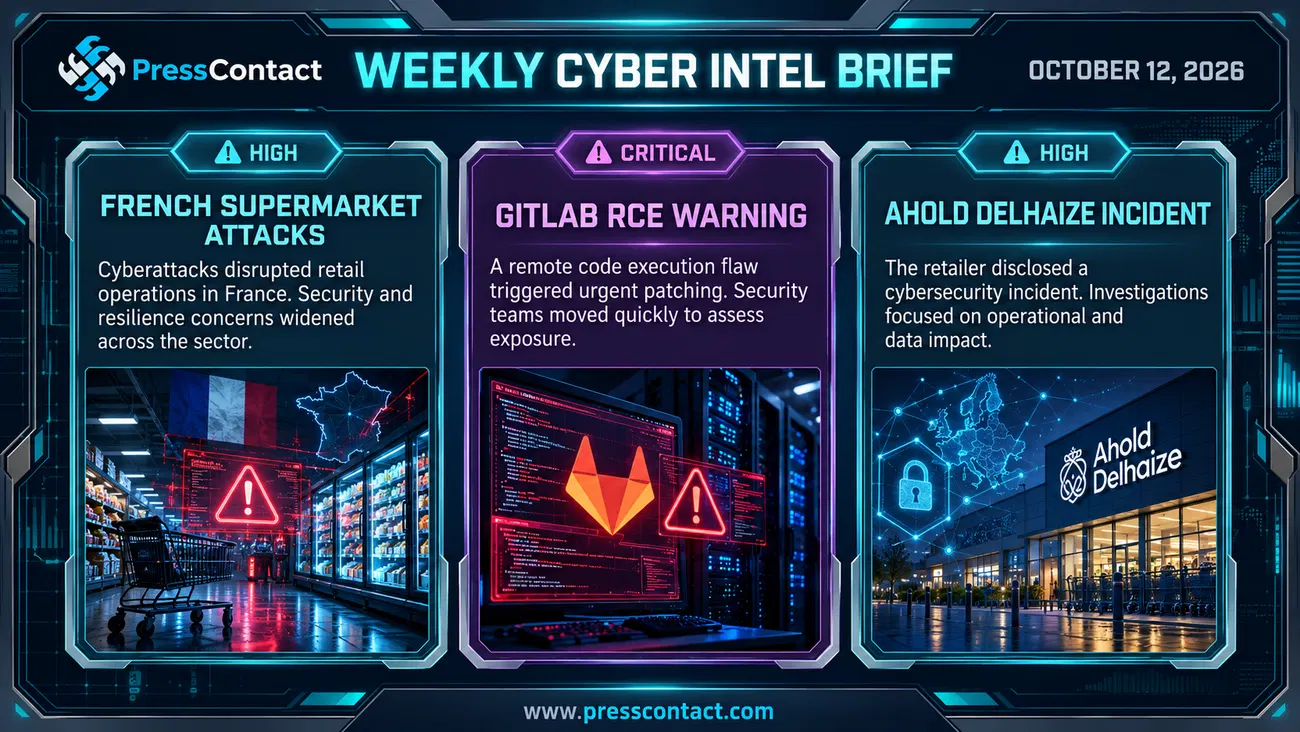
**Cover specification:** Three image compartments: (1) commercial refrigeration controls, (2) CI/CD pipeline / server deployment, (3) grocery retail enterprise operations. Label illustrations as conceptual, not actual evidence. Use an approved original PressContact Cyber Intel master, correct date and exact unmodified logo asset.
**Status:** Unpublished. Specific primary source links checked October 25, 2026; the refrigeration bulletin’s October 13 update is identified above.